


Microsoft SC-300 Exam Prep Guide: Prep guide for the SC-300 Exam
2024 New Preparation Guide of Microsoft SC-300 Exam
To prepare for the Microsoft SC-300 exam, candidates are recommended to have hands-on experience with Azure AD and Azure services, as well as a deep understanding of identity and access management concepts. Microsoft offers a range of training resources, including instructor-led courses, self-paced online training, and practice exams, to help candidates prepare for the exam. Passing the Microsoft SC-300 exam validates the candidate’s expertise in identity and access management and demonstrates their ability to effectively manage identity and access solutions in Microsoft Azure. Microsoft Identity and Access Administrator certification is highly valued by employers and can help individuals advance their careers in the field of cloud-based identity and access management.
NEW QUESTION # 114
You have an Azure Active Directory (Azure AD) tenant that contains a user named User1 and the groups shown in the following table.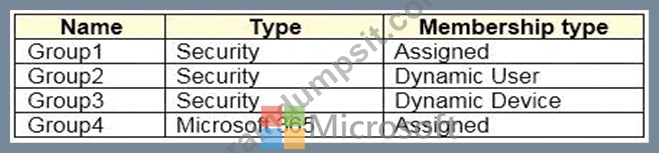
In the tenant, you create the groups shown in the following table.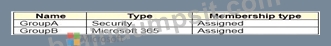
Which members can you add to GroupA and GroupB? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.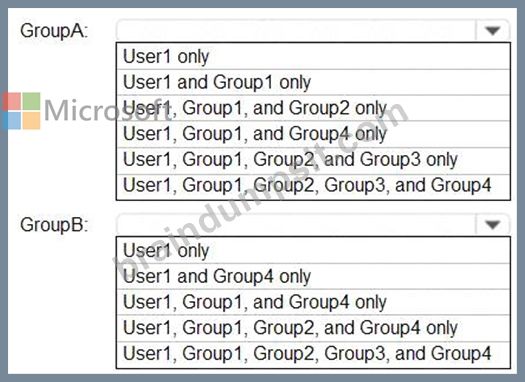
Answer:
Explanation: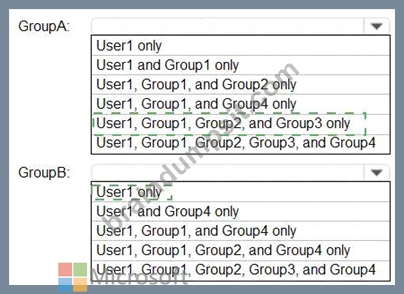
Explanation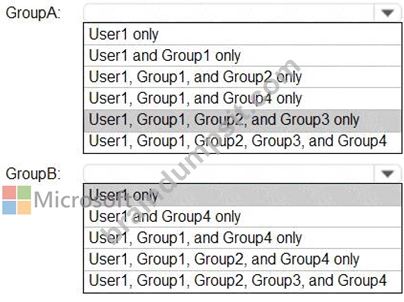
Reference:
https://bitsizedbytes.wordpress.com/2018/12/10/distribution-security-and-office-365-groups-nesting/
NEW QUESTION # 115
Your company has an Azure Active Directory (Azure AD) tenant named contoso.com. The company has a business partner named Fabrikam, Inc.
Fabrikam uses Azure AD and has two verified domain names of fabrikam.com and litwareinc.com. Both domain names are used for Fabrikam email addresses.
You plan to create an access package named package1 that will be accessible only to the users at Fabrikam.
You create a connected organization for Fabrikam.
You need to ensure that the package1 will be accessible only to users who have fabrikam.com email addresses.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.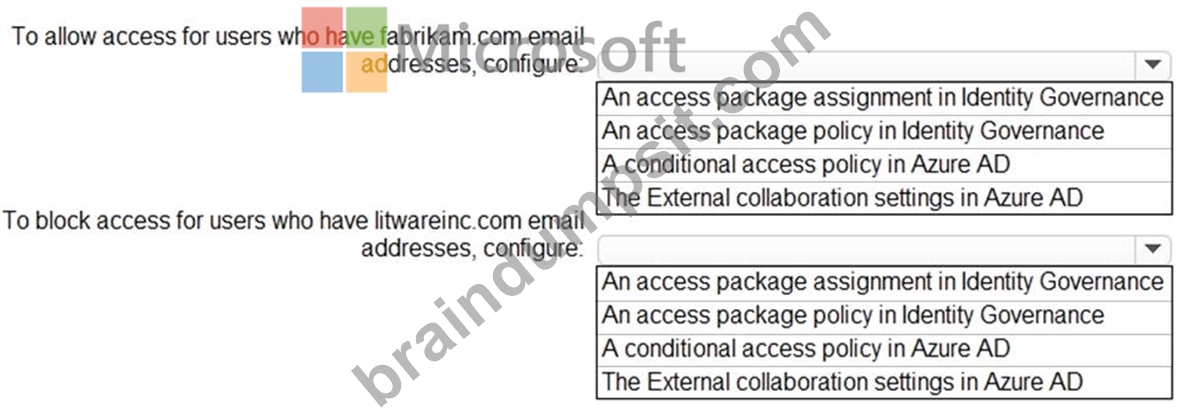
Answer:
Explanation: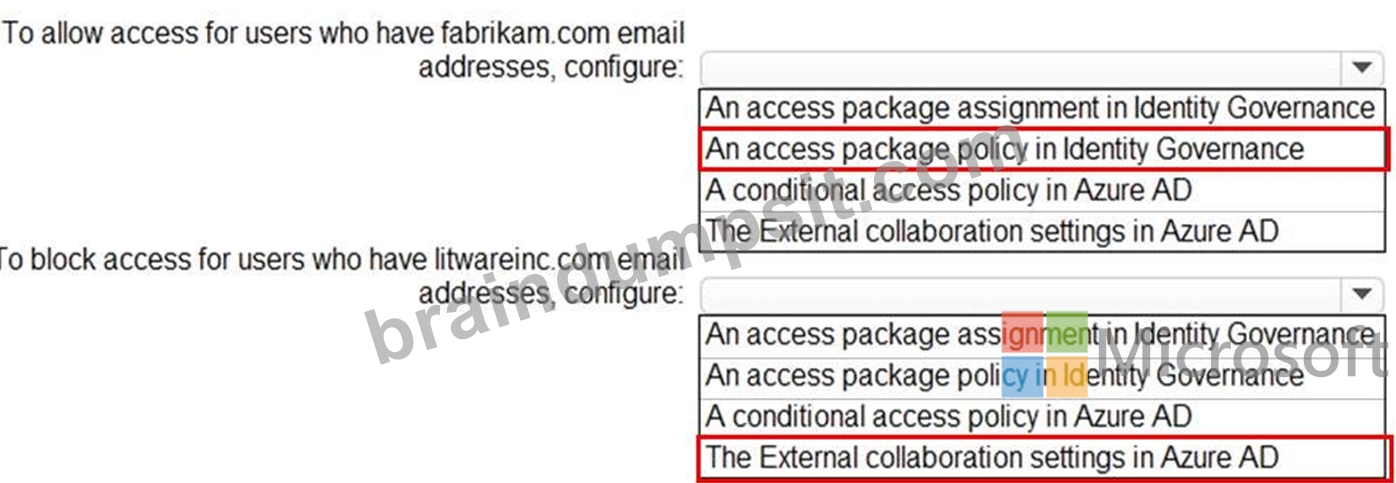
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/governance/entitlement-management-access-package-request-policy
https://docs.microsoft.com/en-us/azure/active-directory/governance/entitlement-management-access-package-create
NEW QUESTION # 116
You need to meet the technical requirements for license management by the helpdesk administrators.
What should you create first, and which tool should you use? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.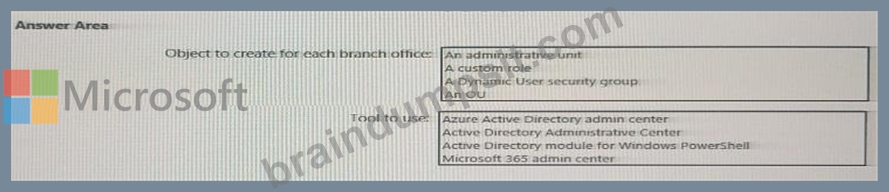
Answer:
Explanation: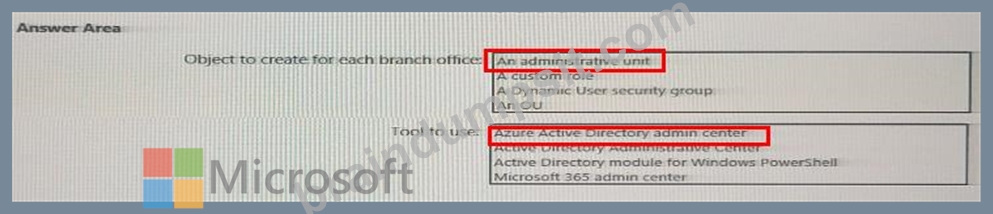
NEW QUESTION # 117
You need to implement password restrictions to meet the authentication requirements.
You install the Azure AD password Protection DC agent on DC1.
What should you do next? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.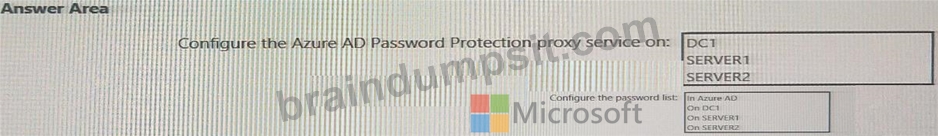
Answer:
Explanation: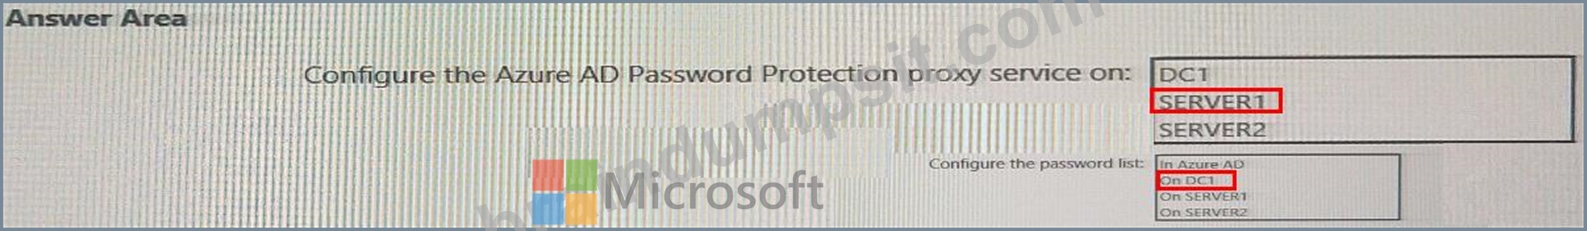
Topic 2, Contoso, Ltd
Existing Environment
The on-premises network of Contoso contains an Active Directory domain named contos.com. The domain contains an organizational unit (OU) named Contoso_Resources. The Contoso_Resoureces OU contains all users and computers.
The Contoso.com Active Directory domain contains the users shown in the following table.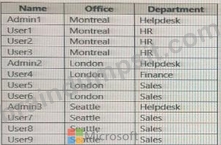
Microsoft 365/Azure Environment
Contoso has an Azure AD tenant named Contoso.com that has the following associated licenses:
Microsoft Office 365 Enterprise E5
Enterprise Mobility + Security
Windows 10 Enterprise E5
Project Plan 3
Azure AD Connect is configured between azure AD and Active Directory Domain Serverless (AD DS). Only the Contoso Resources OU is synced.
Helpdesk administrators routinely use the Microsoft 365 admin center to manage user settings.
User administrators currently use the Microsoft 365 admin center to manually assign licenses, All user have all licenses assigned besides following exception:
The users in the London office have the Microsoft 365 admin center to manually assign licenses. All user have licenses assigned besides the following exceptions:
The users in the London office have the Microsoft 365 Phone System License unassigned.
The users in the Seattle office have the Yammer Enterprise License unassigned.
Security defaults are disabled for Contoso.com.
Contoso uses Azure AD Privileged identity Management (PIM) to project administrator roles.
Problem Statements
Contoso identifies the following issues:
* Currently, all the helpdesk administrators can manage user licenses throughout the entire Microsoft 365 tenant.
* The user administrators report that it is tedious to manually configure the different license requirements for each Contoso office.
* The helpdesk administrators spend too much time provisioning internal and guest access to the required Microsoft 365 services and apps.
* Currently, the helpdesk administrators can perform tasks by using the: User administrator role without justification or approval.
* When the Logs node is selected in Azure AD, an error message appears stating that Log Analytics integration is not enabled.
Planned Changes
Contoso plans to implement the following changes.
Implement self-service password reset (SSPR). Analyze Azure audit activity logs by using Azure Monitor-Simplify license allocation for new users added to the tenant. Collaborate with the users at Fabrikam on a joint marketing campaign. Configure the User administrator role to require justification and approval to activate.
Implement a custom line-of-business Azure web app named App1. App1 will be accessible from the internet and authenticated by using Azure AD accounts.
For new users in the marketing department, implement an automated approval workflow to provide access to a Microsoft SharePoint Online site, group, and app.
Contoso plans to acquire a company named Corporation. One hundred new A Datum users will be created in an Active Directory OU named Adatum. The users will be located in London and Seattle.
Technical Requirements
Contoso identifies the following technical requirements:
* AH users must be synced from AD DS to the contoso.com Azure AD tenant.
* App1 must have a redirect URI pointed to https://contoso.com/auth-response.
* License allocation for new users must be assigned automatically based on the location of the user.
* Fabrikam users must have access to the marketing department's SharePoint site for a maximum of 90 days.
* Administrative actions performed in Azure AD must be audited. Audit logs must be retained for one year.
* The helpdesk administrators must be able to manage licenses for only the users in their respective office.
* Users must be forced to change their password if there is a probability that the users' identity was compromised.
NEW QUESTION # 118
You have a Microsoft 365 tenant that contains a group named Group! as shown in the Group1 exhibit. (Click the Group 1 tab.)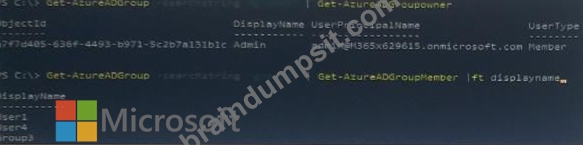
You create an enterprise application named App1 as shown in the App1 Properties exhibit. (Click the App1 Properties tab.)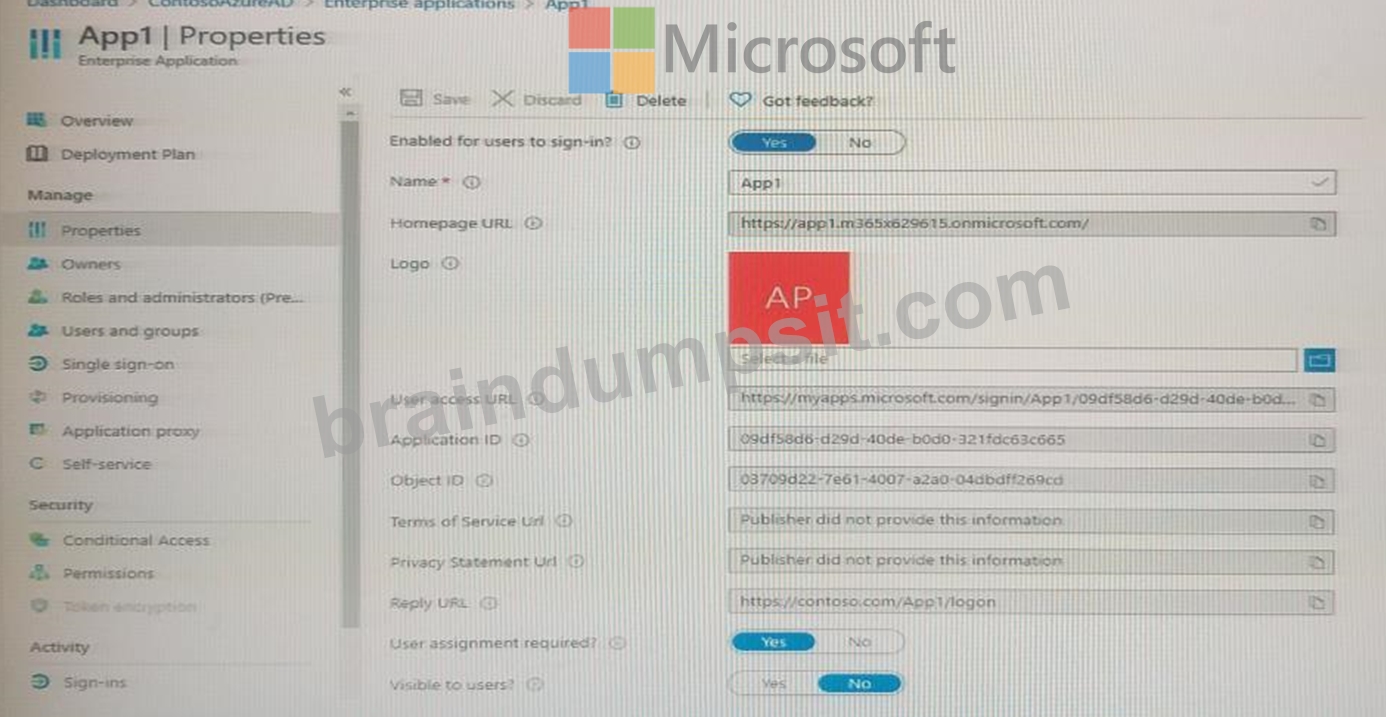
You configure self-service for App1 as shown in the App1 Self-service exhibit: (Click the App1 Self-service tab.)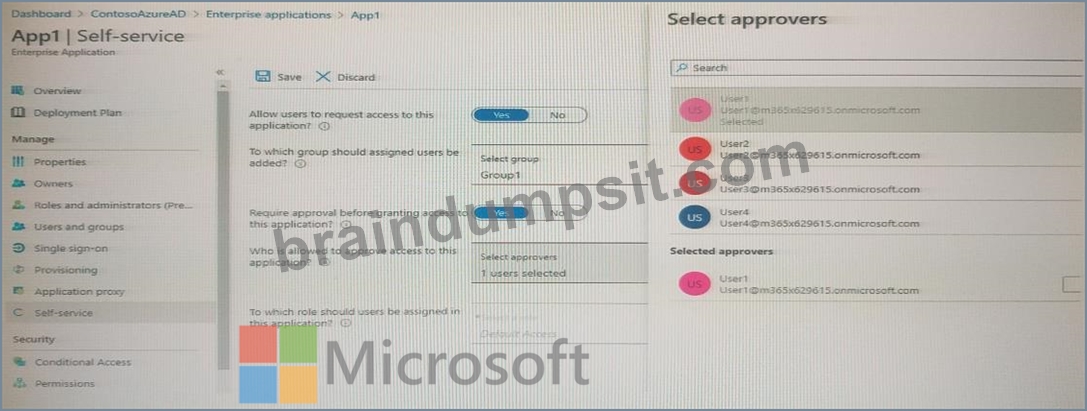
For each of the following statements, select Yes if the statement is true, Otherwise select NO.
NOTE: Each correct selection is worth one point.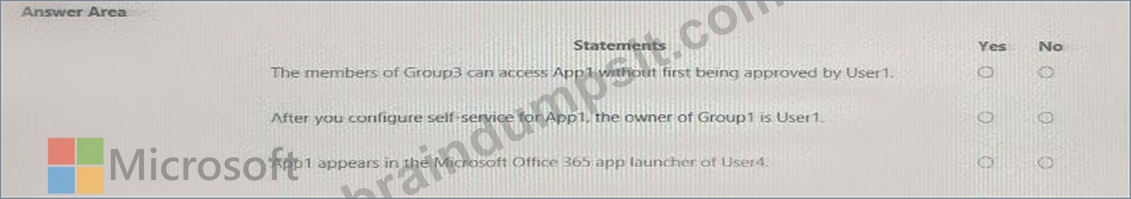
Answer:
Explanation: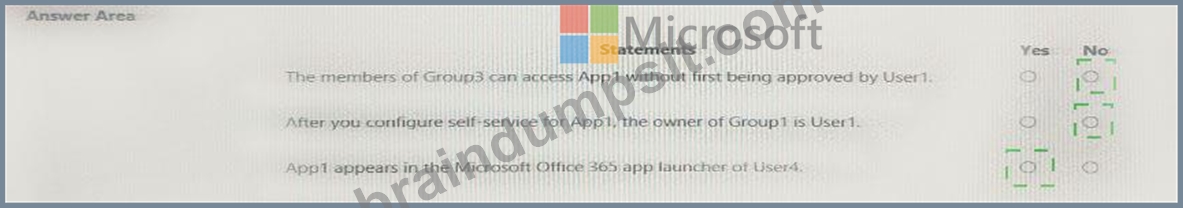
NEW QUESTION # 119
You have an Azure Active Directory (Azure AD) tenant.
You configure self-service password reset (SSPR) by using the following settings:
* Require users to register when signing in: Yes
* Number of methods required to reset: 1
What is a valid authentication method available to users?
- A. an email to an address in your organization
- B. mobile app notification
- C. home prions
- D. a mobile app code
Answer: A
NEW QUESTION # 120
A user named User1 attempts to sign in to the tenant by entering the following incorrect passwords:
Pa55w0rd12
Pa55w0rd12
Pa55w0rd12
Pa55w.rd12
Pa55w.rd123
Pa55w.rd123
Pa55w.rd123
Pa55word12
Pa55word12
Pa55word12
Pa55w.rd12
You need to identify how many sign-in attempts were tracked for User1, and how User1 can unlock her account before the 300-second lockout duration expires.
What should identify? To answer, select the appropriate
NOTE: Each correct selection is worth one point.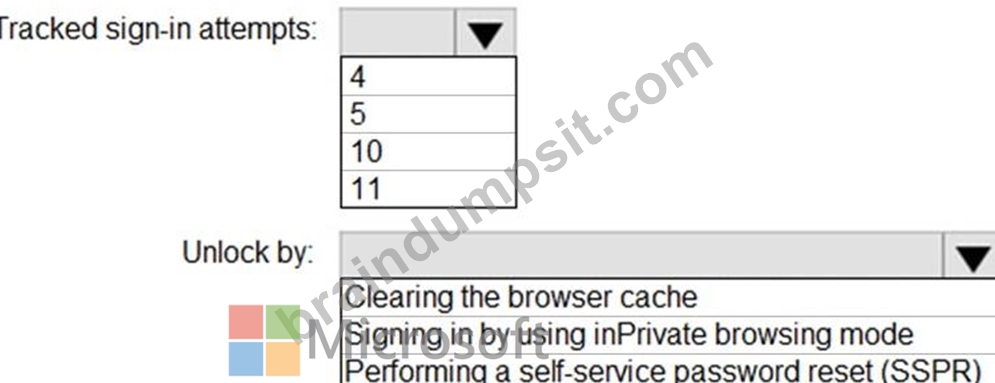
Answer:
Explanation: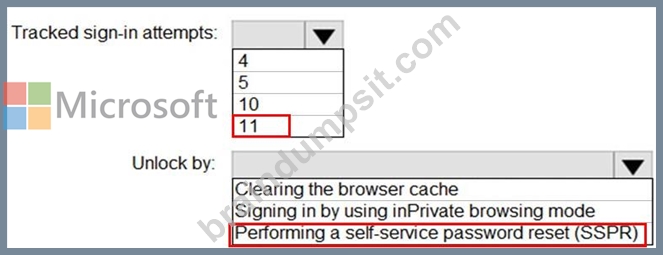
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/authentication/howto-sspr-deployment
NEW QUESTION # 121
You have a Microsoft 365 tenant named contoso.com.
Guest user access is enabled.
Users are invited to collaborate with contoso.com as shown in the following table.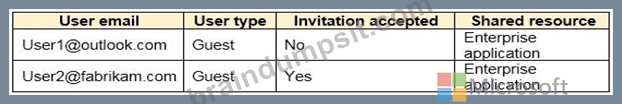
From the External collaboration settings in the Azure Active Directory admin center, you configure the Collaboration restrictions settings as shown in the following exhibit.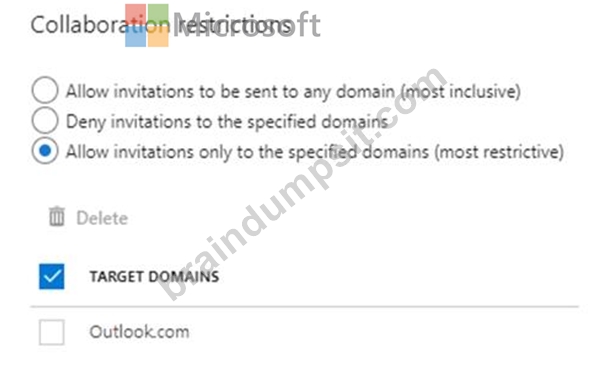
From a Microsoft SharePoint Online site, a user invites [email protected] to the site.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.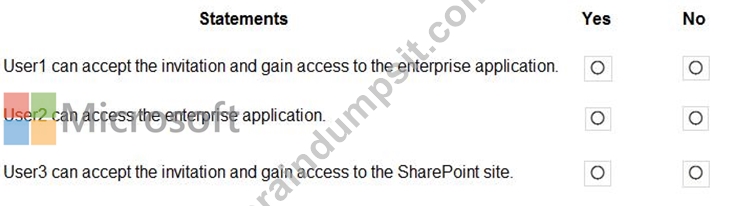
Answer:
Explanation: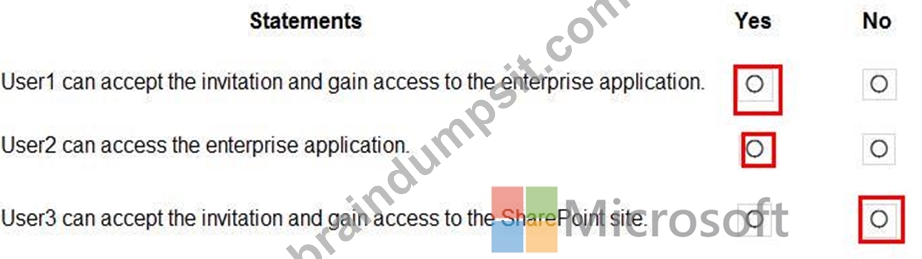
NEW QUESTION # 122
You need to configure the assignment of Azure AD licenses to the Litware users. The solution must meet the licensing requirements.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.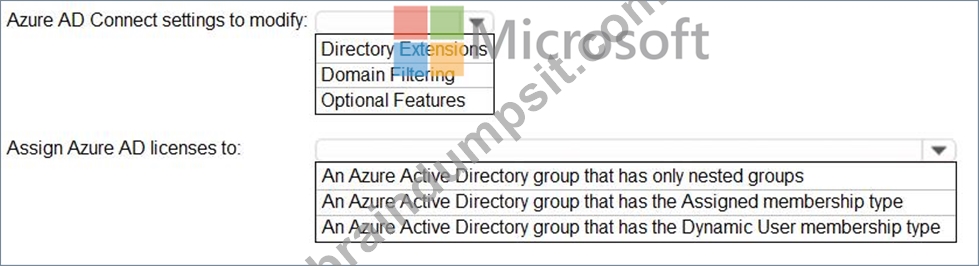
Answer:
Explanation: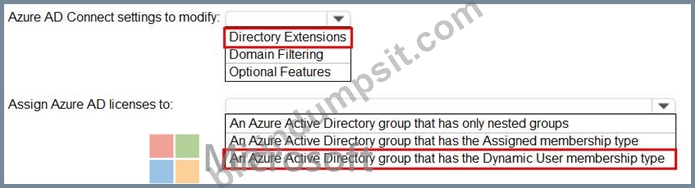
NEW QUESTION # 123
You need to meet the planned changes for the User administrator role.
What should you do?
- A. Create an administrator unit.
- B. Modify Active Assignments.
- C. Modify Role settings
- D. Create an access review.
Answer: B
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/privileged-identity-management/pim-how-to-add-role-to-user?tabs=new
NEW QUESTION # 124
You have an Azure subscription that uses Azure AD Privileged Identity Management (PIM).
You need to identify users that are eligible for the Cloud Application Administrator role.
Which blade in the Privileged Identity Management settings should you use?
- A. Privileged access groups
- B. Azure AD roles
- C. Azure resources
- D. Review access
Answer: B
NEW QUESTION # 125
You have a custom cloud app named App1 that is registered in Azure Active Directory (Azure AD).
App1 is configured as shown in the following exhibit.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/manage-apps/assign-user-or-group-access-portal
NEW QUESTION # 126
Your network contains an on-premises Active Directory domain that syncs to an Azure Active Directory (Azure AD) tenant. The tenant contains the users shown in the following table.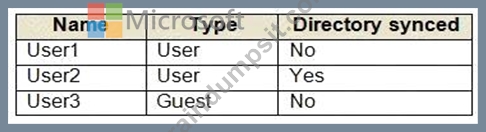
All the users work remotely.
Azure AD Connect is configured in Azure AD as shown in the following exhibit.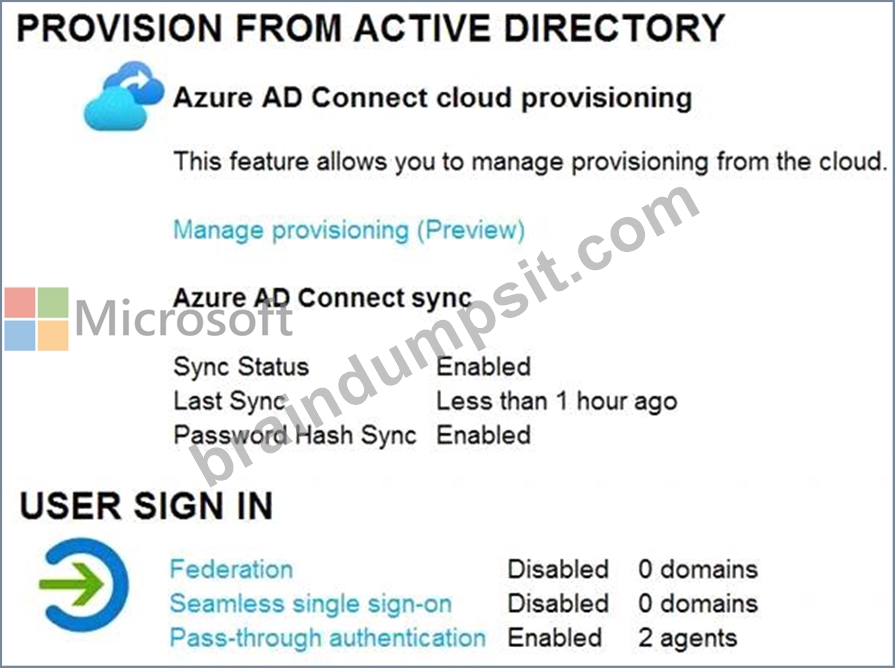
Connectivity from the on-premises domain to the internet is lost.
Which users can sign in to Azure AD?
- A. User1 and User3 only
- B. User1, User2, and User3
- C. User1 and User2 only
- D. User1 only
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/hybrid/how-to-connect-pta-current-limitations
NEW QUESTION # 127
You have an Azure AD tenant that contains the users shown in the following table.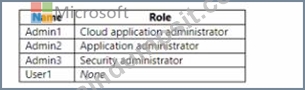
You add an enterprise application named App1 to Azure AD and set User1 as the owner of App1 requires admin consent to access Azure AD before the app can be used.
You configure the Admin consent requests strong as shown in the following exhibit.
Admin consent requests.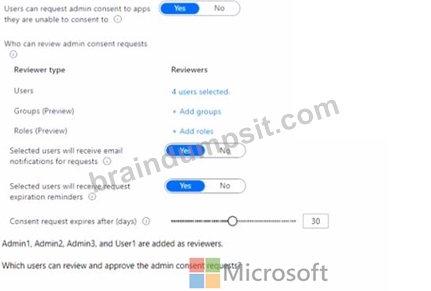
- A. Admln1, Admin2. and User1 only
- B. Admm1 and Admin2 only
- C. Admm1 Admm2 and Admin3 only
- D. Admm1 only
- E. Admm1 Admm2. Admm3, and User1
Answer: B
NEW QUESTION # 128
You have an Azure Active Directory (Azure AD) tenant that has multi-factor authentication (MFA) enabled.
The account lockout settings are configured as shown in the following exhibit.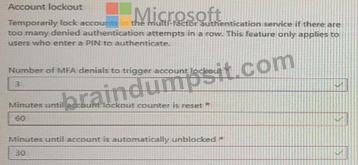
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.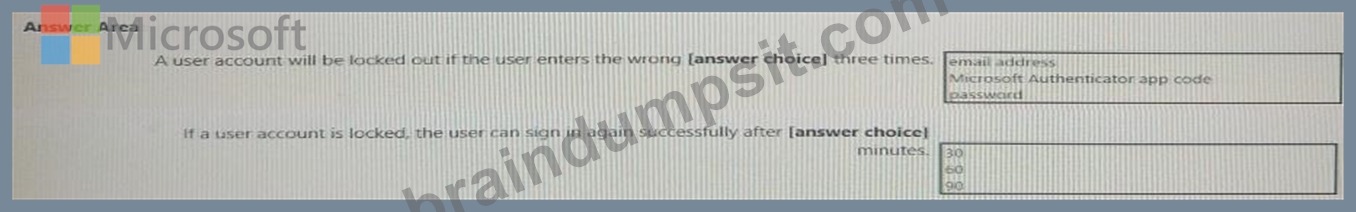
Answer:
Explanation: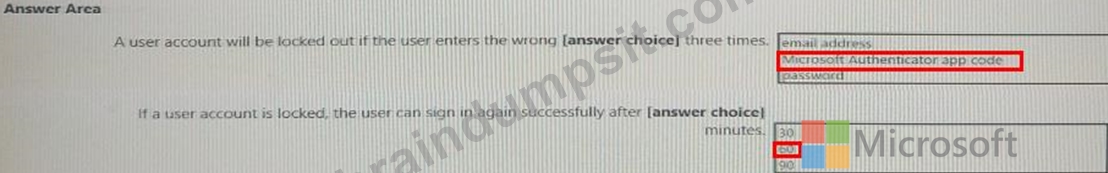
NEW QUESTION # 129
You have a Microsoft 36S tenant.
You create a named location named HighRiskCountries that contains a list of high-risk countries.
You need to limit the amount of time a user can stay authenticated when connecting from a high-risk country.
What should you configure in a conditional access policy? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.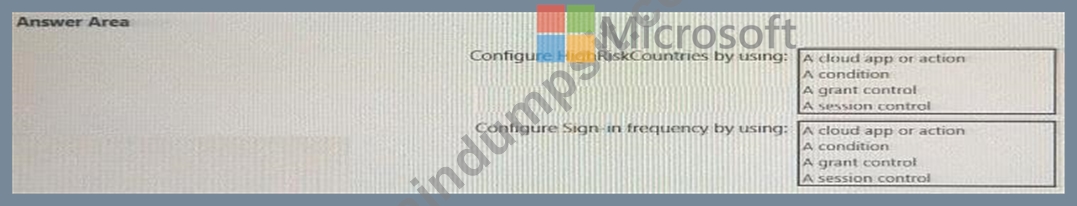
Answer:
Explanation: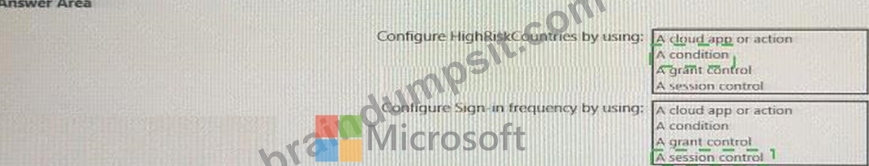
Explanation
Graphical user interface, text, application Description automatically generated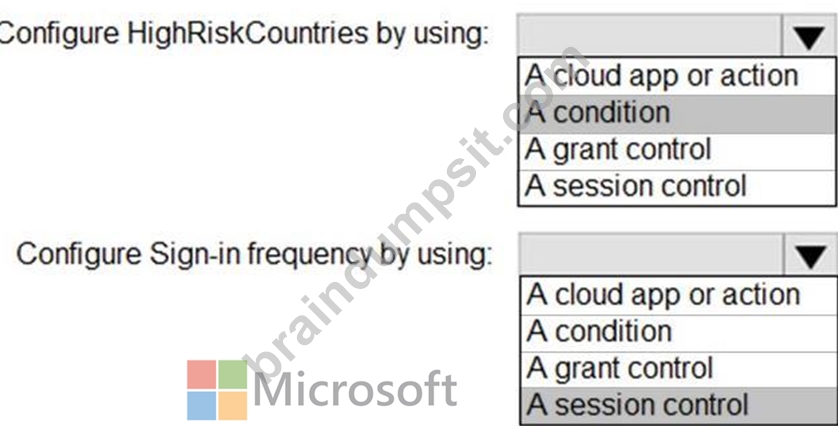
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/conditional-access/location-condition
https://docs.microsoft.com/en-us/azure/active-directory/conditional-access/concept-conditional-access-session
NEW QUESTION # 130
You have an Azure AD tenant that contains the users shown in the following table.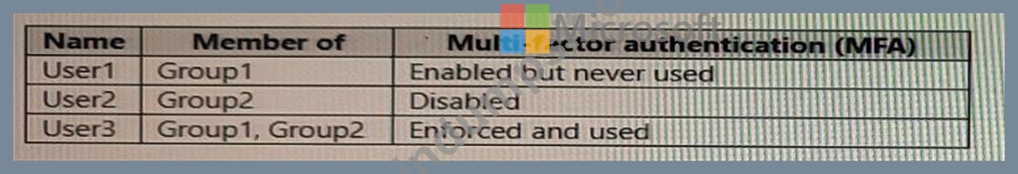
In Azure AD Identity Protection, you configure a user risk policy that has the following settings:
* Assignments:
o Users: Group1
o User risk: Low and above
* Controls:
o Access: Block access
* Enforce policy: On
In Azure AD Identity Protection, you configure a sign-in risk policy that has the following settings:
* Assignments:
o Users: Group2
o Sign-in risk: Low and above
* Controls:
o Access: Require multi-factor authentication
* Enforce policy. On
the following settings:
ng settings:
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.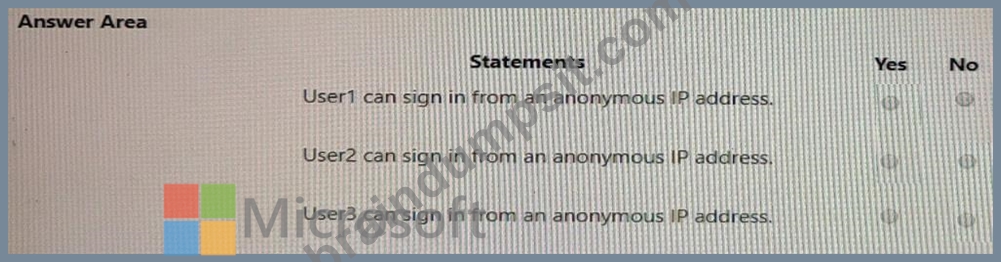
Answer:
Explanation: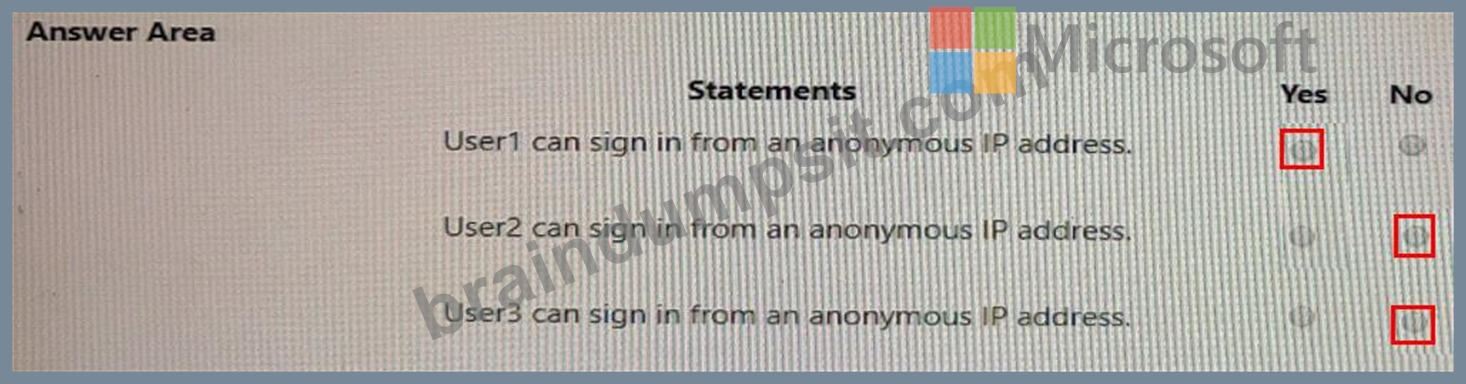
NEW QUESTION # 131
......
Latest Questions SC-300 Guide to Prepare Free Practice Tests: https://www.braindumpsit.com/SC-300_real-exam.html
SC-300 Practice Exam - 285 Unique Questions: https://drive.google.com/open?id=1MU1stP098GO8ir3PtmUXHcSYzdJMcX59